The USDC in Washington has just issued a decision on specific personal jurisdiction over a Web site operator. In running through the typical analysis of how much the defendant aimed its activity at the forum state, the court held that the operator's site "was expressly aimed at Washington in that the website lists Washington as an available shipping location and Defendant intentionally shipped its product into this state . . .."
This after noting that only three of the plush dolls at issue had been shipped to Washington, out of the 22 total states where the Michigan-based defendant had sold its products. (Arguably, the three shipments alone might have tipped the balance, but I think some courts would have had a tough time with that as the only factor.)
So, a convenience offered to users of web sites that is not offered to people who fill-in little coupons out of a magazine suddenly subjects the retailer to jurisdiction. Who knew the Web was going to be so dangerous?
It seems unlikely that the vendor who probably sold the off-the-shelf shopping cart system to the defendant here took the time to note that including any particular state in the drop-down list was going to subject the defendant to the personal jurisdiction of every state in that list. It also seems a bit of a stretch to fathom the defendant's intent out of what was probably nothing more than a choice made by the shopping cart operator (who was merely following the standard practice for all shopping carts). Should we now be counseling our clients that they should not present a dropdown list of states to anybody? Or, is the convenience to the site's customers worth the risk (but the lawyers to the site need to counsel on the risk in any event)? Should shopping cart developers provide a functionality in their software to allow site operator to delete certain states from the list? Should the site operator bring a claim against the shopping cart vendor for a design defect? (Just kidding on that last one...) (Sort of...)
Second practice note: Keep in mind that this is not a case where a click-through choice of law/venue provision would have made a difference, since the plaintiff was not itself a customer of the defendant's site nor subject to any contract between it and the defendant. We can't always rely on those contracts to save us from all possible exposure to out-of-state litigation!
Case is Qwest Communications Int., Inc. v. Sonny Corp. (USDC WD Wash NO. C06-20P, May 15, 2006). Reported in the June 15 issue of BNA Electronic Commerce Reporter.
Wednesday, June 14, 2006


Monday, May 15, 2006
SCOTUS to Trolls: Go Home?
There is a bit of a bombshell for the patent bar on the Supreme Court's front porch today -- No doubt the folks at RIM are a bit miffed that this didn't occur about 3 months ago, but I digress...
Have Justices Kennedy, Stevens, Souter and Breyer all but given public recognition to the (so-called) patent troll industry? Read into the following whatever you might like...
Have Justices Kennedy, Stevens, Souter and Breyer all but given public recognition to the (so-called) patent troll industry? Read into the following whatever you might like...
In cases now arising trial courts should bear in mind that in many instances the nature of the patent being enforced and the economic function of the patent holder present considerations quite unlike earlier cases. An industry has developed in which firms use patents not as a basis for producing and selling goods but, instead, primarily for obtaining licensing fees. See FTC, To Promote Innovation: The Proper Balance of Competition and Patent Law and Policy, ch. 3, pp. 38-39 (Oct. 2003), available at http://www.ftc.gov/os/2003/10/innovationrpt.pdf (as visited May 11, 2006, and available in Clerk of Court's case file). For these firms, an injunction, and the potentially serious sanctions arising from its violation, can be employed as a bargaining tool to charge exorbitant fees to companies that seek to buy licenses to practice the patent. See ibid. When the patented invention is but a small component of the product the companies seek to produce and the threat of an injunction is employed simply for undue leverage in negotiations, legal damages may well be sufficient to compensate for the infringement and an injunction may not serve the public interest. In addition injunctive relief may have different consequences for the burgeoning number of patents over business methods, which were not of much economic and legal significance in earlier times. The potential vagueness and suspect validity of some of these patents may affect the calculus under the four-factor test.
EBAY INC. et al. v. MERCEXCHANGE, L. L. C., ___ U.S. ___ (May 15, 2006) (J. Kennedy concurrence)(emphasis added).
Saturday, May 13, 2006
8th Circuit Rules in Case Involving Digitally Enhanced Evidence
In U.S. v. Seifert, the U.S. Court of Appeals for the Eighth Circuit ruled on the admissibility of video evidence that had been digitally altered to brighten the image. The original images were very dark. An expert used software tools to brighten the entire image, which then showed a suspect who was dressed very much like the defendant.
So, fellow lawyers, add Photoshop to your list of essential software skills on your resumes.
The case is here.
So, fellow lawyers, add Photoshop to your list of essential software skills on your resumes.
The case is here.
Friday, May 12, 2006
No More Pesky 8x10 Enlargement Spam
No, not that kind of enlargement. Get your mind out of the gutter.
In a clear victory over the photolab spammer cadre, the FTC has once again shown us the immense value and public good that has come to us out of the CAN-SPAM Act. Kodak Imaging Network sent out an e-mail to 2 million recipients that failed to contain an opt-out mechanism, failed to disclose the right to opt-out, and failed to include a valid physical postal address. For this, they paid over $26 grand in penalties and have the watching eye of the FTC to contend with for the next few years.
So -- I have no doubt the marketer did the dastardly deed (as I gather from the rapid closure that Kodak did not dispute the facts). Take that as a lesson learned for them, as well as for the rest of us who are advising clients on how to comply with CAN-SPAM. Fair enough.
But was this what we thought we were getting when we passed a law about spam? 'Gotcha' cases against legitimate companies that make dumb mistakes as opposed to something that has a meaningful impact on the mess that flows into our inboxes every day? How many of us have spent time complaining to our loved ones about the burden of deleting great masses of photo-lab spams? Are the fake-pharmacy-spammers really going to read about this case and suddenly realize they need to alter their marketing methods to comply with the law?
If anything, this action by FTC -- if this is the best they can come up with -- seems to almost prove the ineffectiveness of CAN-SPAM to achieve its original purpose.
In any event, please be sure to tell your clients to include the opt-out and address! See 15 U.S.C. § 7704(a)(5)(A)!
In a clear victory over the photolab spammer cadre, the FTC has once again shown us the immense value and public good that has come to us out of the CAN-SPAM Act. Kodak Imaging Network sent out an e-mail to 2 million recipients that failed to contain an opt-out mechanism, failed to disclose the right to opt-out, and failed to include a valid physical postal address. For this, they paid over $26 grand in penalties and have the watching eye of the FTC to contend with for the next few years.
So -- I have no doubt the marketer did the dastardly deed (as I gather from the rapid closure that Kodak did not dispute the facts). Take that as a lesson learned for them, as well as for the rest of us who are advising clients on how to comply with CAN-SPAM. Fair enough.
But was this what we thought we were getting when we passed a law about spam? 'Gotcha' cases against legitimate companies that make dumb mistakes as opposed to something that has a meaningful impact on the mess that flows into our inboxes every day? How many of us have spent time complaining to our loved ones about the burden of deleting great masses of photo-lab spams? Are the fake-pharmacy-spammers really going to read about this case and suddenly realize they need to alter their marketing methods to comply with the law?
If anything, this action by FTC -- if this is the best they can come up with -- seems to almost prove the ineffectiveness of CAN-SPAM to achieve its original purpose.
In any event, please be sure to tell your clients to include the opt-out and address! See 15 U.S.C. § 7704(a)(5)(A)!
Tuesday, April 11, 2006
Working Group on International Policy
The Working Group on International Policy met on Saturday morning under the experienced leadership of Hal Burman. He circulated a couple of e-commerce-related documents from the Organization of American States, proposed for the next private international law meeting of the OAS. The two, one from Brazil and one from Canada, dealt with jurisdiction in consumer matters in e-commerce. State Dept would be interested in comments on them. U.S. is inclined to prefer the Canadian proposal, at least as basis for discussion. (There is also an FTC proposal on small claims that is not directed at cyberspace issues.)
The OAS documents are on the Internet Jurisdiction and Global E-Commerce subcommittee's home page, under Other Links of Interest:
http://www.abanet.org/dch/committee.cfm?com=CL320060
Most of the discussion focused on the UNCITRAL Convention on the use of electronic communications in international contracts. The Subcommittee yesterday approved joining the Science and Technology Section in supporting US signature of the Convention. Hal's meeting went in more detail into the signature process and the different considerations that might have to be taken into account in a decision whether to ratify the convention.
The Executive Director, Bill Henning, and the past president, Fred Miller, of NCCUSL were present, along with several veterans of the UETA process, to discuss whether and how NCCUSL might express its views on the Convetion. Bill indicated that NCCUSL would usually restrict itself to saying that the Convention was compatible with state law, rather than actively supporting the Convention.
Pat Fry and others would study the Convention in early May and report to the Committee and to State on their views.
The meeting discussed how the proposal to support signing might be presented to the Council of the Section, and the timing of this in light of NCCUSL's timetable. It was thought that the Committee should take this forward to COuncil, with help from the International Coordinating Committee, without waiting for the NCCUSL review, if Cyberspace had done its own (which we consider ourselves to have done). Council might send views on to State or it might wait to see what NCCUSL had to say - it was certainly of interest to Council whether NCCUSL had concerns. Hal and Henry Gabriel suggested that the Convention was very much like UETA and should not be problematic.
Several members of the Working Group, along with Candace J, were bound from there to the International Coordinating Committee to make their case, which your blogger can now report they did, and their plea was supported at that Committee - particularly in light of the limit of the proposal to support signature only at this stage.
The OAS documents are on the Internet Jurisdiction and Global E-Commerce subcommittee's home page, under Other Links of Interest:
http://www.abanet.org/dch/committee.cfm?com=CL320060
Most of the discussion focused on the UNCITRAL Convention on the use of electronic communications in international contracts. The Subcommittee yesterday approved joining the Science and Technology Section in supporting US signature of the Convention. Hal's meeting went in more detail into the signature process and the different considerations that might have to be taken into account in a decision whether to ratify the convention.
The Executive Director, Bill Henning, and the past president, Fred Miller, of NCCUSL were present, along with several veterans of the UETA process, to discuss whether and how NCCUSL might express its views on the Convetion. Bill indicated that NCCUSL would usually restrict itself to saying that the Convention was compatible with state law, rather than actively supporting the Convention.
Pat Fry and others would study the Convention in early May and report to the Committee and to State on their views.
The meeting discussed how the proposal to support signing might be presented to the Council of the Section, and the timing of this in light of NCCUSL's timetable. It was thought that the Committee should take this forward to COuncil, with help from the International Coordinating Committee, without waiting for the NCCUSL review, if Cyberspace had done its own (which we consider ourselves to have done). Council might send views on to State or it might wait to see what NCCUSL had to say - it was certainly of interest to Council whether NCCUSL had concerns. Hal and Henry Gabriel suggested that the Convention was very much like UETA and should not be problematic.
Several members of the Working Group, along with Candace J, were bound from there to the International Coordinating Committee to make their case, which your blogger can now report they did, and their plea was supported at that Committee - particularly in light of the limit of the proposal to support signature only at this stage.
Yet Another Candid Camera Moment from Roland
My -- I give this guy the right to post and he just goes way overboard...
(Many thanks to Roland who really did a great job of adding to our blogging output this meeting. Let us all encourage him to continue, and to bring along that cool little camera of his as well. Here's a shot taken at the Carlton Fields reception outside the Yacht StarShip.)

(Many thanks to Roland who really did a great job of adding to our blogging output this meeting. Let us all encourage him to continue, and to bring along that cool little camera of his as well. Here's a shot taken at the Carlton Fields reception outside the Yacht StarShip.)
Saturday, April 08, 2006
A few glimpses from the Columbia Restaurant -- The Committee Dinner
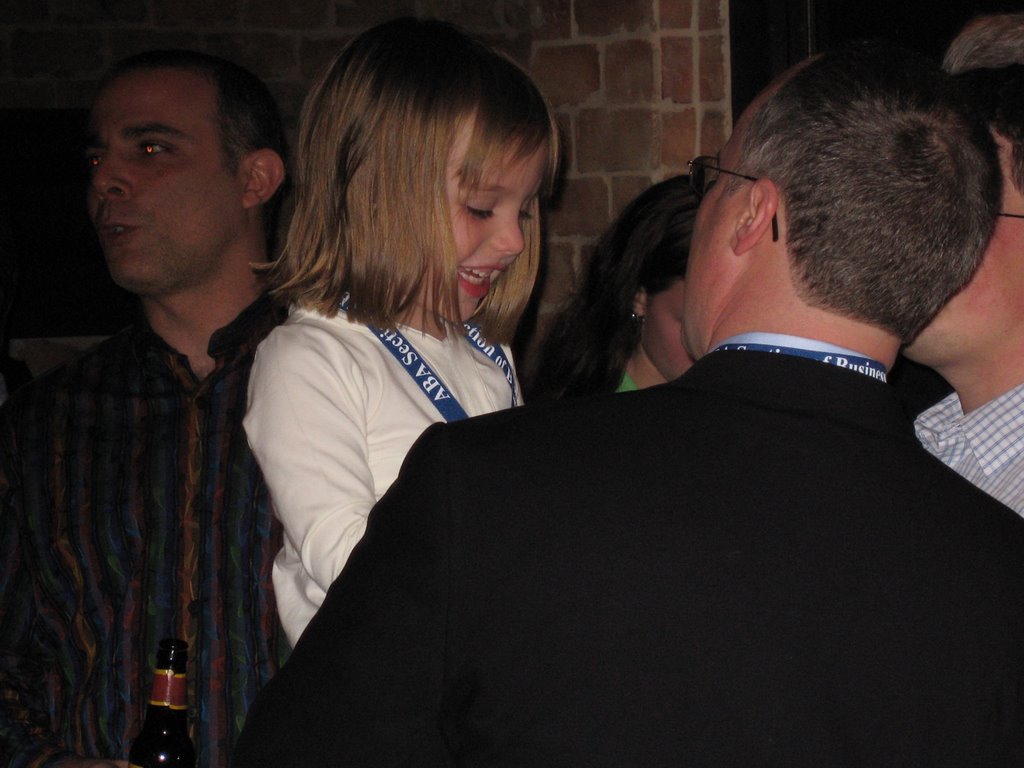 Michael Fleming and his daughter
 Ray Gustini
 Juliet Moringiello
 Jonathan Armstrong (leveraging his British accent)
We {heart} Ziff
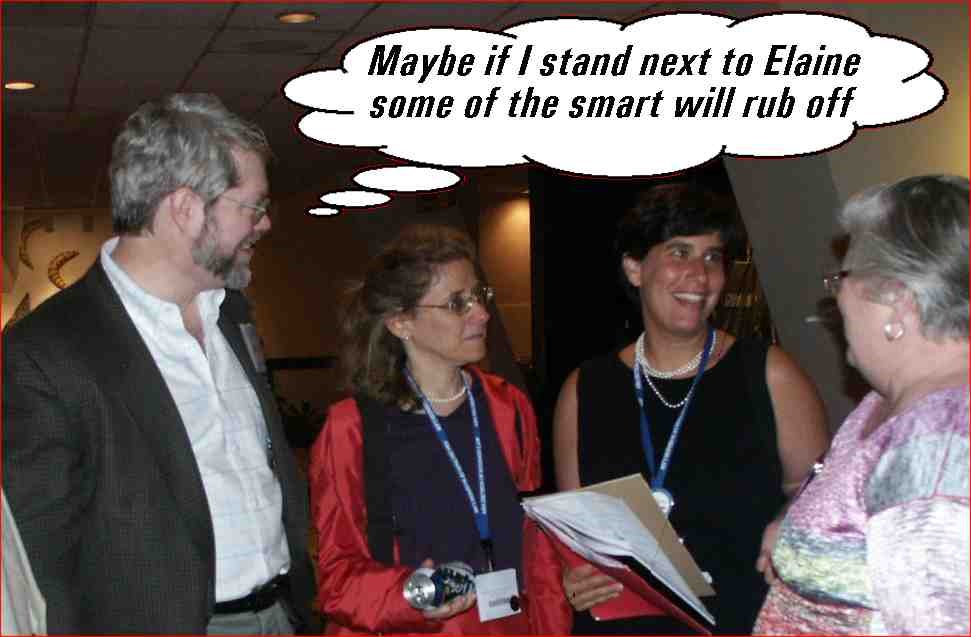
Sometime around 2001 as I was walking from one subsubsubworking group to another, at the Cyberspace Winter Working Group meeting at the DC Capital Hilton, I ran into this woman who was cruising the emptying room picking up the handout at the end of a session. (You know, the I-was-in-one- meeting-but-there-was- this-other-one- I-really-wanted-to-see- so-I-dropped-by-the-room -to-see-if-they-left- any-handouts ABA scavenger hunt. C'mon, don't tell me you don't do it too.) Literally ran into her, and I think I had to pick up the pile of paper we both dropped. I gave her the short version:
(insert Polley inflection here, boots optional) "Cyberspace Committee, ABA, Internet, all kinds of new law, e-commerce good, people good, fun good, publications pretty good."
I got most of the details wrong -- a point of which she still reminds me ("you said it was TWO years as chair! You LIED!") pretty much every ABA meeting -- but we hit it off anyway. Only thing I did right was to reflexively reach out to a newcomer. But hey, she bought it -- and became a wonderful leader, key Cyberspace author, replaced me and outdid me, and herself became the incubator of a bunch of additional really good leaders.
Today is her last day as E-Commerce Committee chair and we should celebrate her successes. Luckily someone booked us into a Cuban bar for dinner tonight... See you in Ybor City.
Afternoon Excursion (before Cyberspace Committee Dinner)
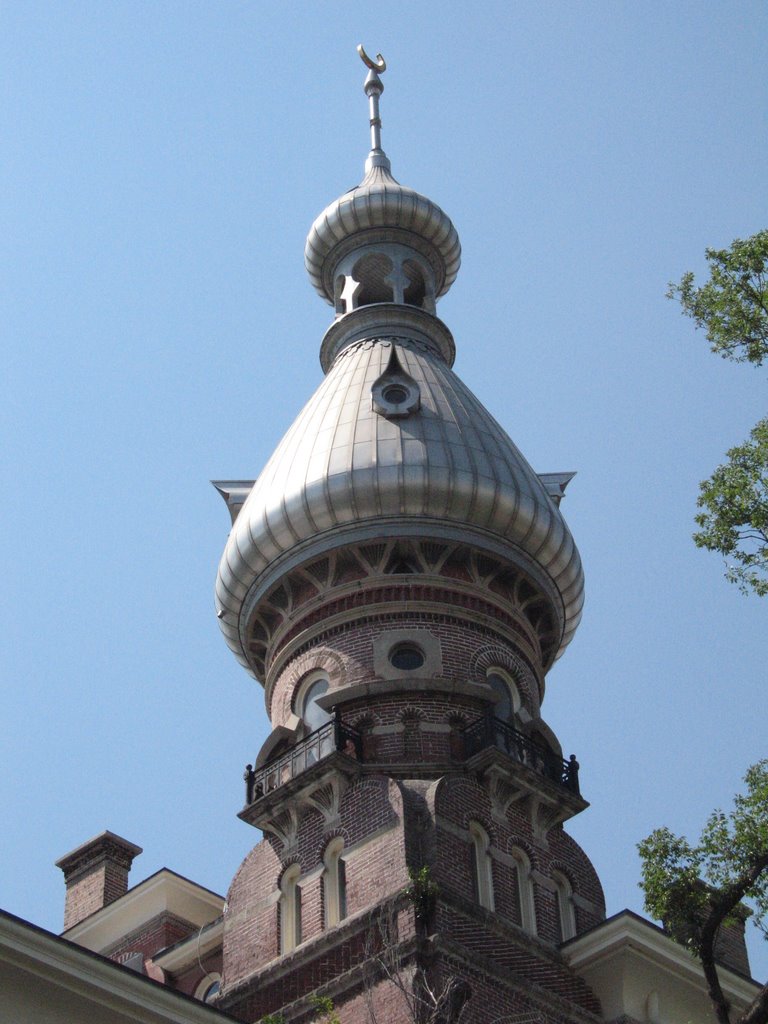
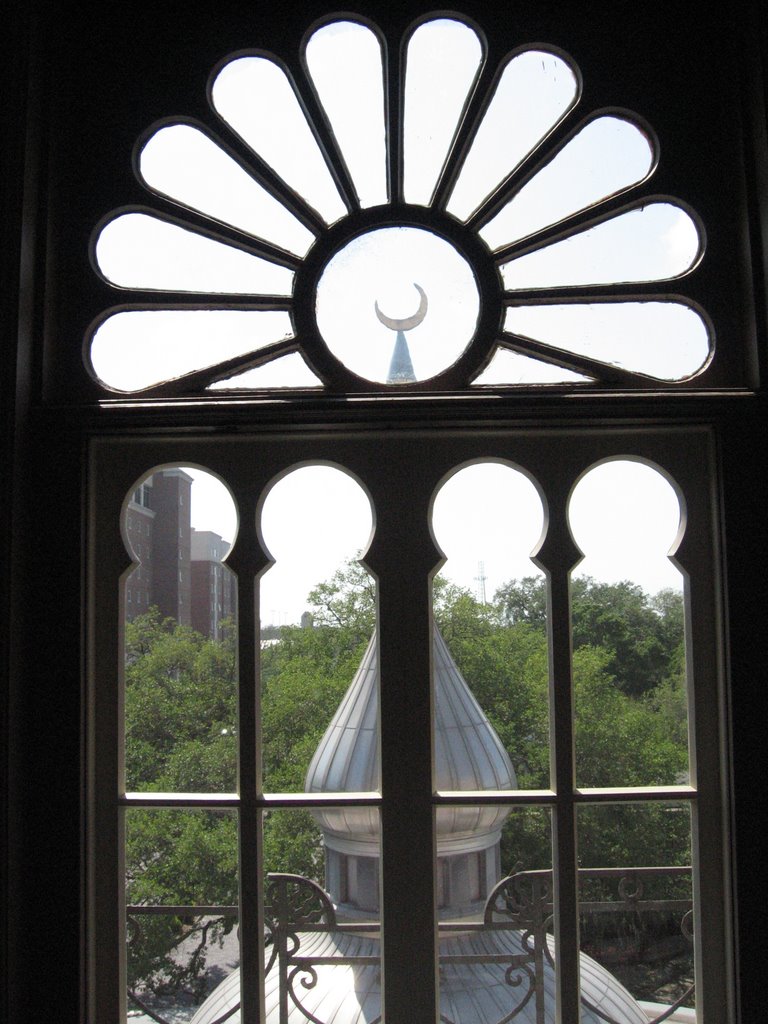
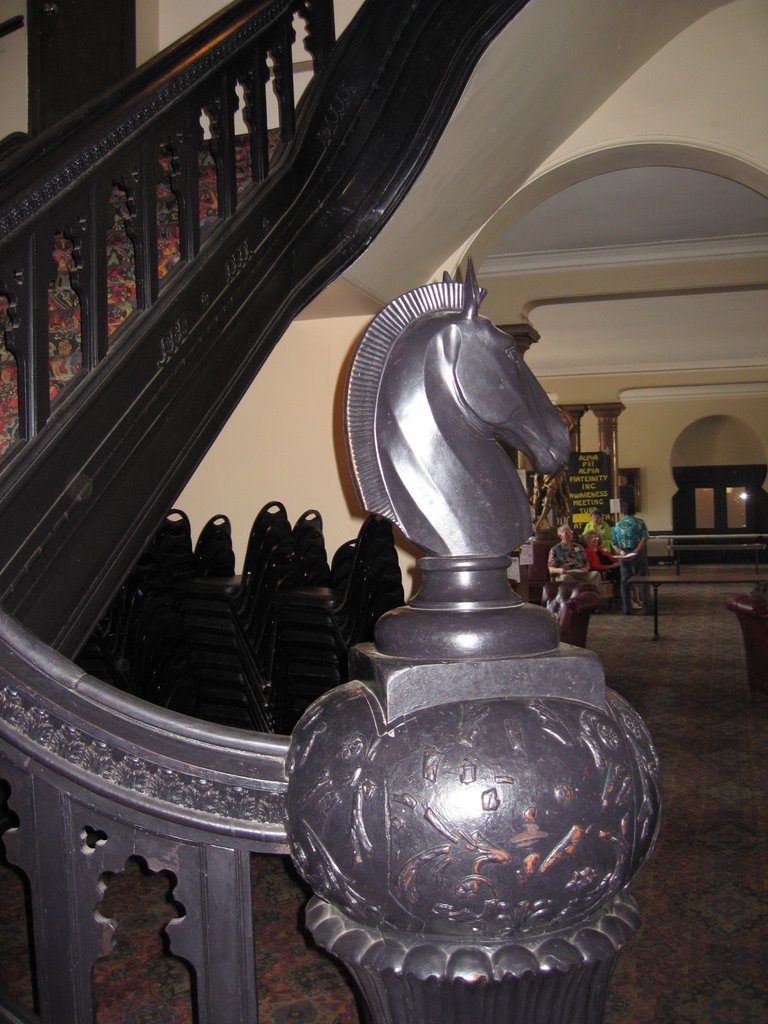
An intrepid group of cyberspace counsel fortified themselves with water, sunscreen and umbrellas and walked (some would say trekked) to the nearby Henry B. Plant Museum and its exotic architecture. Photos are better than words to describe the Museum, which was formerly a railroad hotel and is now known as Florida's First Magic Kingdom.

PROGRAM: 21st Century Risks and Age-Old Insurance Clauses
Bill Denny led a very interesting program how businesses are responding (or, in many instances, not responding) to the risks arising out of participating in cyberspace.
Mike Rodman of Albert Risk Management Consultants spoke on his observations of businesses and how they interact with the need for cyber-insurance. He noted a number of risks that should be addressed in any useful policy, particularly noting the need to address what things are NOT covered in other policies such as CGL. He suggested that there is still a lack of belief in the need for these kinds of cyber-loss policies -- and that in his opinion businesses do that at a higher degree of risk than they believe.
Bill Denny spoke on traditional contract principles and how we have historically allocated risks in IT deals. He then recalled the traditional insurance policies that we might have been analyzing for our clients -- third-party liability policies including CGL and its cousin E&O to cover many traditional IP claims such as copyright infringement; and first party coverages such as property, automobile and the like. He reminded us of the differences between occurence policies versus claims-made policies. He also reminded us of how some policies provide defense, some do not, some will pay defense costs after the claim is actually paid out, some count defense costs against the policy limits while others do not. Bill also went over how much of the boilerplate provisions we frequently glaze over may be self-defeating of our purported intentions.
Margaret Reetz of Chicago discussed how the newer policies have been working out in practice, based on her practice representing insurers. She discussed concepts of how the cyber-policies provide coverage, and misconceptions that are out there.
Emily Freeman of JLT Risk Solutions of London discussed how so many of us will spend so much time negotiating the best indemnity clause ever written, and never take the time to wonder if the indemnifying party has any insurance to stand behind that indemnity. She reminded us again how 'useless' CGL policies will be to cover indemnified cyber-risks. She also reminded us of how little consistency there is between the various policies that fall into the so-called cyber-policies. Her strongest message was that we should never rely on just calling out the name of a policy (like "CyberInsurance") and assuming that any particular risks are covered. (Emily has a checklist she would be willing to offer that lists the various risks that we should be asking about.) Rather, we need to cite the specific risks that need to be covered. She discussed the methods that potential insureds will need to follow to get coverage, including the due diligence that insurers will do prior to writing coverage. (Getting coverage, and 'passing' due diligence by the underwriter, is itself a flag for customers of the insured parties. Failure to get insurance can be a red flag.) She also noted that those who rely on their vendors to be the sole source of potential assets to cover risks are potentially foolish. The sorts of claims involve actions that tend to harm many parties -- Imagine a privacy breach that causes thousands of consumers who have dozens of different banks, all of whom use a common financial data services provider. If that provider has a $5 million policy, there is not much left for the 2nd claimant after all 4 dozen of them suffer $5 million in damages. Those customer businesses will hope they had through to obtain their own policies.
Mike Rodman of Albert Risk Management Consultants spoke on his observations of businesses and how they interact with the need for cyber-insurance. He noted a number of risks that should be addressed in any useful policy, particularly noting the need to address what things are NOT covered in other policies such as CGL. He suggested that there is still a lack of belief in the need for these kinds of cyber-loss policies -- and that in his opinion businesses do that at a higher degree of risk than they believe.
Bill Denny spoke on traditional contract principles and how we have historically allocated risks in IT deals. He then recalled the traditional insurance policies that we might have been analyzing for our clients -- third-party liability policies including CGL and its cousin E&O to cover many traditional IP claims such as copyright infringement; and first party coverages such as property, automobile and the like. He reminded us of the differences between occurence policies versus claims-made policies. He also reminded us of how some policies provide defense, some do not, some will pay defense costs after the claim is actually paid out, some count defense costs against the policy limits while others do not. Bill also went over how much of the boilerplate provisions we frequently glaze over may be self-defeating of our purported intentions.
Margaret Reetz of Chicago discussed how the newer policies have been working out in practice, based on her practice representing insurers. She discussed concepts of how the cyber-policies provide coverage, and misconceptions that are out there.
Emily Freeman of JLT Risk Solutions of London discussed how so many of us will spend so much time negotiating the best indemnity clause ever written, and never take the time to wonder if the indemnifying party has any insurance to stand behind that indemnity. She reminded us again how 'useless' CGL policies will be to cover indemnified cyber-risks. She also reminded us of how little consistency there is between the various policies that fall into the so-called cyber-policies. Her strongest message was that we should never rely on just calling out the name of a policy (like "CyberInsurance") and assuming that any particular risks are covered. (Emily has a checklist she would be willing to offer that lists the various risks that we should be asking about.) Rather, we need to cite the specific risks that need to be covered. She discussed the methods that potential insureds will need to follow to get coverage, including the due diligence that insurers will do prior to writing coverage. (Getting coverage, and 'passing' due diligence by the underwriter, is itself a flag for customers of the insured parties. Failure to get insurance can be a red flag.) She also noted that those who rely on their vendors to be the sole source of potential assets to cover risks are potentially foolish. The sorts of claims involve actions that tend to harm many parties -- Imagine a privacy breach that causes thousands of consumers who have dozens of different banks, all of whom use a common financial data services provider. If that provider has a $5 million policy, there is not much left for the 2nd claimant after all 4 dozen of them suffer $5 million in damages. Those customer businesses will hope they had through to obtain their own policies.
Subscribe to:
Posts (Atom)
