Although time zone issues will probably impede many of us on this side of the world from participating live, this site:
http://igf2006.intgovforum.org/
is open for business and allows one to monitor the Internet Governance Forum taking place in Greece right now. If you register, you can monitor live feeds, read and participate in chats, and all that other good Web 2.0 stuff.
The Internet Governance Forum is the continuing discussion that arose out of the meeting in Tunisia last year, which itself was part of the World Summit on the Information Society (WSIS) set up by the UN and the ITU. Many of our members have worked to understand the original mandate of the WSIS and its ongoing efforts through IGF.
Remember, our own members David Satola and Kristine Dorrain are live and on the ground at the Athens meeting, and will be presenting to the crowd on legal issues this coming Wednesday at 9:30 AM Athens time (which is, unfortunately, about 1:30 in the morning my own time, so I regret that I'll have to read about it in the papers the next day).
UPDATE: Dave Satola reports to me that all is going well at the Summit. Still, there are some troubles to be had apparently... United Nations "Internet" Summit held sans internet
Monday, October 30, 2006


Wednesday, October 18, 2006
Open Source Continues to Come of Age
cNet notes that "OpenLogic, a provider of open-source software for enterprises, is offering indemnification against legal action for companies using its code." The company does note that its indemnity no longer applies if the indemnitee has modified the code in the OpenLogic code. And, the operating system used (e.g., Linux) is not covered by the OpenLogic indemnity (although there may be policies available from insurers, such as Lloyds, to cover that). So, the end user still has some degree of patching together risk-allocation tools in order to create a reasonably protected system.
Still, the days when lawyers in the know should just instantly panic when they hear about OS in their clients' houses should be deemed as officially over. Our own committee's members recently presented a very well-received program on how to assess open source as a risk during a corporate merger transaction -- materials available here (ABA Business Law Section members only).
Like everything else we do, there is still plenty of work to do to make sure the hatches are battened down. However, the coming of age of the OS industry means that the lawyers can start to add value by pointing out the risk management tools their clients can use, and help them to negotiate or assess actual risk versus falling into abject panic.
Still, the days when lawyers in the know should just instantly panic when they hear about OS in their clients' houses should be deemed as officially over. Our own committee's members recently presented a very well-received program on how to assess open source as a risk during a corporate merger transaction -- materials available here (ABA Business Law Section members only).
Like everything else we do, there is still plenty of work to do to make sure the hatches are battened down. However, the coming of age of the OS industry means that the lawyers can start to add value by pointing out the risk management tools their clients can use, and help them to negotiate or assess actual risk versus falling into abject panic.
Saturday, October 07, 2006
Wendy's Blog: Legal Tags: Coming Soon: Kitten with a EULA?
The title of Wendy's blog post (quoted above in this posting's own title) gets it slightly wrong. They don't require you to sign a "license agreement," but they do require that you agree to a rather lengthy contract before they'll allow you to purchase their specially bred hypoallergenic cat. The contract contains a rather broad indemnity clause, a restriction that you not let the cat wander outside or suffer a waiver of any warranties, restrictions on further sale, etc. They also claim patent rights in the cats. Whew.
Thursday, September 14, 2006
Software Doesn't Need to be Perfect?
The company that makes the self-balancing Segway scooters (the two-wheeler for people) announced on September 14 that it is recalling all 23,500 of the units it has shipped to date "because of a software glitch that can make its wheels unexpectedly reverse direction, causing riders to fall off."
As discussed in prior posts, we have come to expect a lesser standard of care in the provision of software -- The sort of thing that we would never find acceptable in other areas such as how our airplanes work. Maybe this story reminds us that those two concepts are more or less impossible to sever in practice, since there are all too many physical products that may potentially injure us that are dependent themselves on software.
That much was probably obvious already to anybody who can reach this blog. What it should also suggest to those of us practicing in cyberspace is that our willingness to let our deals go forward where the software providers to a larger project are held to a lower standard than the provider of the project as a whole. If the software provider for a car's computer suggests that it cannot take liability for what might go wrong with the car, then what is the car manufacturer to do that needs that software? Should it decide that it cannot afford the cost of the vendor's sure-thing software guaranty? Should it decide that it must ultimately bring the project in-house because it can't afford to allow quality control to lie in a third-party who is not willing to be on the hook? Should it calculate the risk of a problem and insure against it rather than try to avoid fixing the problem?
These are often seemingly irresolveable problems for buyers and sellers, although that may be a reflection of the consumer willingness to pay for safety versus whether or not it can be done. That said, understanding these issues and now to describe and negotiate them are what our subset of the profession can offer to the move the debate beyond what today is often simply a battle of wills.
As discussed in prior posts, we have come to expect a lesser standard of care in the provision of software -- The sort of thing that we would never find acceptable in other areas such as how our airplanes work. Maybe this story reminds us that those two concepts are more or less impossible to sever in practice, since there are all too many physical products that may potentially injure us that are dependent themselves on software.
That much was probably obvious already to anybody who can reach this blog. What it should also suggest to those of us practicing in cyberspace is that our willingness to let our deals go forward where the software providers to a larger project are held to a lower standard than the provider of the project as a whole. If the software provider for a car's computer suggests that it cannot take liability for what might go wrong with the car, then what is the car manufacturer to do that needs that software? Should it decide that it cannot afford the cost of the vendor's sure-thing software guaranty? Should it decide that it must ultimately bring the project in-house because it can't afford to allow quality control to lie in a third-party who is not willing to be on the hook? Should it calculate the risk of a problem and insure against it rather than try to avoid fixing the problem?
These are often seemingly irresolveable problems for buyers and sellers, although that may be a reflection of the consumer willingness to pay for safety versus whether or not it can be done. That said, understanding these issues and now to describe and negotiate them are what our subset of the profession can offer to the move the debate beyond what today is often simply a battle of wills.
Wednesday, September 06, 2006
You Might Want to Look it up Before You Go to Court
In an interesting little case at the 8th Circuit involving the intersection between 'computer program' and 'data' and the application of the Computer Software Rental Amendments Act of 1990, the court took pains to suggest that the lawyer arguing the case at District Court for the (alleged...) copyright holder did not even understand a fundamental concept in the world of copyright registration:
Oops. I would not want to presume anything about whomever was arguing the case, since it may have been a last minute substitution. But, there was obviously a mishandling of the registration of the copyright (and, maybe I need to reconsider my rule-of-thumb that lawyers are rarely needed in actual registration practice for copyright). It clearly is a lesson for the rest of us -- These technicalities are important but oft-times relegated to the last minute if at all.
Although the case ended up turning on a technicality (failure to register the copyright prior to litigation), the court did offer some thoughts on the underlying theories suggesting that it would have likely decided the case against the copyright holder in any event. The case involved a company that made programs that controlled sewing machines making patterns. The program uses memory cards that contained the instructions for the pattern that was being sewed. A retailer made a habit of lending out memory cards to her customers (although unstated in the opinion, I presume that the computer program itself was not lent out, just the memory cards with the instructions).
The copyright holder sued, claiming that the lending out of the memory cards was an infringement based on the Rental Act's prohibition on lending out copies of 'computer programs' (a specific statutory exemption from the first sale doctrine). The defendant argued that the memory cards did not comprise a 'computer program,' and therefore were still subject to the plain old First Sale Doctrine rules (which allow one to lend, rent or otherwise dispose of a particular authorized copy of a work once it has first been sold under the authority of the copyright holder). The District Court agreed and granted summary judgment on that basis. The 8th Circuit did not reach the question since it noted that the registration used by the plaintiff was not properly done for a 'computer program,' which, among other things, requires that the source code for the program be filed with the registration (which had not been done) -- Thus, deciding the case on the ground that the plaintiff had no case because it "failed to prove it applied for registration of the computer program copyrights before commencing this infringement suit." The plaintiff tried to duck the problem by noting that it still held a valid copyright in the visual design, and again the court noted that even if that were true the exemption from the first sale doctrine only applies to computer programs and not to visual designs.
Although our group focuses on our 'cyberspace' commonality, many of us are frequently brought in for intellectual property concerns, and particularly where computer programs or the like are involved. Or, rather -- We should be brought in. Yet another reason to seek out attorneys who have the knowledge and background to know what Source Code might be...
Indeed, the term source code is nowhere to be found in Action Tapes’ pleadings and motion papers, and at the summary judgment motion argument counsel did not know the meaning of that term.
Oops. I would not want to presume anything about whomever was arguing the case, since it may have been a last minute substitution. But, there was obviously a mishandling of the registration of the copyright (and, maybe I need to reconsider my rule-of-thumb that lawyers are rarely needed in actual registration practice for copyright). It clearly is a lesson for the rest of us -- These technicalities are important but oft-times relegated to the last minute if at all.
Although the case ended up turning on a technicality (failure to register the copyright prior to litigation), the court did offer some thoughts on the underlying theories suggesting that it would have likely decided the case against the copyright holder in any event. The case involved a company that made programs that controlled sewing machines making patterns. The program uses memory cards that contained the instructions for the pattern that was being sewed. A retailer made a habit of lending out memory cards to her customers (although unstated in the opinion, I presume that the computer program itself was not lent out, just the memory cards with the instructions).
The copyright holder sued, claiming that the lending out of the memory cards was an infringement based on the Rental Act's prohibition on lending out copies of 'computer programs' (a specific statutory exemption from the first sale doctrine). The defendant argued that the memory cards did not comprise a 'computer program,' and therefore were still subject to the plain old First Sale Doctrine rules (which allow one to lend, rent or otherwise dispose of a particular authorized copy of a work once it has first been sold under the authority of the copyright holder). The District Court agreed and granted summary judgment on that basis. The 8th Circuit did not reach the question since it noted that the registration used by the plaintiff was not properly done for a 'computer program,' which, among other things, requires that the source code for the program be filed with the registration (which had not been done) -- Thus, deciding the case on the ground that the plaintiff had no case because it "failed to prove it applied for registration of the computer program copyrights before commencing this infringement suit." The plaintiff tried to duck the problem by noting that it still held a valid copyright in the visual design, and again the court noted that even if that were true the exemption from the first sale doctrine only applies to computer programs and not to visual designs.
Although our group focuses on our 'cyberspace' commonality, many of us are frequently brought in for intellectual property concerns, and particularly where computer programs or the like are involved. Or, rather -- We should be brought in. Yet another reason to seek out attorneys who have the knowledge and background to know what Source Code might be...
Tuesday, September 05, 2006
U.S. District Court Takes Judicial Notice that Computer Services Stink
OK -- They never quite said it that way. But, how else can a cynic like me interpret this quote?
That might seem to make sense at first blush, but how much is that true just because we've become so used to it? Try substituting "airplane passenger service" in place of 'computers and software' in that last sentence -- No court would ever say such a thing. Why is such an important sector of our economy still working under a lax standard of care after many decades of opportunity to standardize systems and interconnections (usually the first excuses given for why a new IT widget won't work in anybody's environment)? (Note that the provider was quick to resort to the courts to enforce it's side of the bargain...)
The decision out of the USDC for Minnesota can be read here.
Although issues may have arisen as to the services provided, there is no plain, clear language in the Service Agreement requiring NBS to implement a system free of bugs without opportunity to remedy technical problems. Reading this type of requirement into any contract involving computers or software would render virtually every provider of computer services or software in breach of their contracts.
That might seem to make sense at first blush, but how much is that true just because we've become so used to it? Try substituting "airplane passenger service" in place of 'computers and software' in that last sentence -- No court would ever say such a thing. Why is such an important sector of our economy still working under a lax standard of care after many decades of opportunity to standardize systems and interconnections (usually the first excuses given for why a new IT widget won't work in anybody's environment)? (Note that the provider was quick to resort to the courts to enforce it's side of the bargain...)
The decision out of the USDC for Minnesota can be read here.
Monday, August 07, 2006
And so the Sun Sets on the Hawaii Annual Meeting

Many thanks to the great number of people who contributed to a great Annual Meeting here in Honolulu -- Members of the committee, members from the rest of the Section and Association, and colleagues from all over the globe.
Hawaii has been quite hospitable to each of us, and many of us have stated our hope to return in the future. Many are packing up today, many more tomorrow (Tuesday), and a few lucky ones are staying on for the rest of the week.
As we all knew, fewer of us could make it to this meeting as we would normally hope to see at an ABA Annual. Because of that, we are especially hoping that many of our friends will be joining us at the next gathering of Cyberspace Committee members in Little Rock, Arkansas this coming January. We are just on the verge of signing our hotel contracts and getting set up for this event, so please keep your travel plans open for the 26th and 27th of January, 2007. Member and Chair of the Malware Working Group Elizabeth Bowles is looking forward to greeting us all to her lovely home town, as well as to introduce us to her soon-to-be new family member (currently baking in the oven as they say).
And, stay tuned to the Blog in the meantime, since we will try to keep you apprised of Committee goings-on as well as the occasional piece of snarky commentary from your editors.
Aloha. And, hang loose cousins.

Final CLC Program of the Meeting
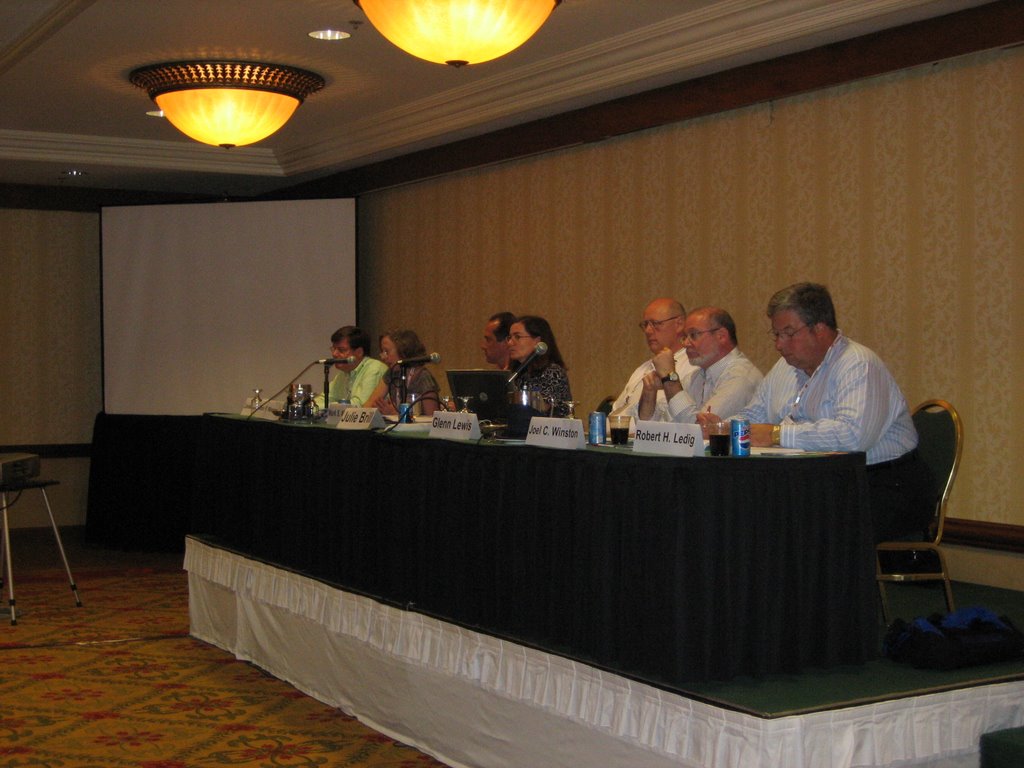
The last of the programs co-sponsored by CLC was held this morning -- "You Had a Security Breach, What Do You Have to Do and What Happens Next?," which was presented by the Consumer Financial Services Committee and co-sponsored by Cyberspace and the Committee on Banking Law. Our own Bob Ledig, seated on the right of the podium area, helped to prepare the panel of experts.
Two representatives from the government enforcement branches (neither of whom, as we all know all too well, was speaking on behalf of either or their respective government entities) helped lay the groundwork for the enforcement authority as well as developing laws in the 'notification of breach' arena (now known as NOB amongst those in the know). A forensic expert took us through many of the preparations that a business should be doing in advance of a problem as well as once the breach has occurred. Finally, an attorney who practices in defending companies who are being sued after a breach has occurred spoke (reminding us that not many of these cases have succeeded as of yet, frequently on the basis that the harm has not come into actuality).
Paper materials ran out early, but Business Section members can download their own copy here. Julie Brill's materials, which provide a great summary, among other things, of the current NOB laws, were updated after the publication date for the CLE materials -- I will be posting a copy of an updated version of those materials here once I receive it.
When will we have the first virtual scalpers?

Apropos our recent discussion of virtual gaming world economies, Boing Boing points out that 80s musical icons Duran Duran have taken a long-term gig playing within the virtual world of the multi-player game Second Life. I don't know who the opening act is yet.
Link.
Sunday, August 06, 2006
Business Meeting of the Committee
Candace opened the second of our two plenary sessions for the CLC in Hawaii -- This one, unlike yesterday which was intended to be our 'substantive' discussion, was intended for committee business.
Rae Cogar and Tim Chorvat discussed their ongoing projects for the Electronic Evidence Working Group. They wish to develop a few short articles for BLT followed by a program for one of our future ABA meetings. Candace suggested that what we need to is find the angle for business lawyers, since otherwise we will be (a) taking on more than we as a committee could chew, and (b) our expertise is not as litigators but rather as business advisors.
(Editor's note: Many lamented that management is not willing to engage in these issues, assuming that this is a lawyer's, and more particularly a litigator's, problem. What gets business managers' attention? If something will cost them money. Remember that system auditing controls were a non-issue until Sarbox came along, and consumer privacy issues were a minor issue for senior managers until the PCI standards came along threatening a merchant's ability to access credit card systems. As the new Federal Rules of Civil Procedure roll out in the next few months, which will be addressing deep-level electronic data concerns in discovery, management will eventually realize this is a bottom line issue. We best be ready to advise once that happens.)
Vince Polley raised the possibility of a project to advise primarily in-house attorneys regarding their companyies' receipt of a National Security Letter from the U.S. government (as provided in the USA-Patriot Act). This proposal would be jointly operated with other ABA constituencies such as the ABA Standing Committee on Law and National Security and the BLS Committee on Banking Law, each of which have indicated interest in working with the Cyberspace Committee. A lively discussion followed, with a few war stories and the like. For the moment, Michael Power and Peter McLaughlin in the Privacy Subcommittee will take the lead on organizing a project, although we will still be thinking about whether this is best in a particular subcommittee or organizing a task force, and maybe even setting up the task force as joint with other ABA groups. -- Stay tuned, but there was clearly a topic of great interest to this group.
Judie Rinearson opened up discussion of her sub-committee's work on how anti-money laundering laws (AML) will impact stored payment systems. Again, we pointed out that we should be looking to collaborate with other groups, such as Consumer Financial Services. Judy heard from others who offered help.
Candace announced that the upcoming Winter Working Meeting will be held in Little Rock, Arkansas. ABA is about to sign a contract with the Doubletree Inn in downtown. We will be pushing committee leadership to plan well ahead. Note that because the Spring Meeting in DC will be March 15-18, which is earlier than usual, we may well be too late at the WWM to prepare materials for Spring. (Unfortunately, we don't have hard deadlines yet, so this is surmise for the moment.)
Candace asked folks who participated in the prior day's CLC meeting, which was the "Un-Conference" format for setting up substantive discussions around the round table. All who were there yesterday thought it was a great exercise. One comment was that the size of the audience was probably important to how it worked, and that a typical full-sized CLC meeting would probably be too large for the format to work.
Candace mentioned the committee is being asked to provide a beta-testing group for the upcoming replacement of the ABA's listserve system (using the Fusetalk platform). A couple of the subcommittees volunteered to be guinea pigs. We will be learning more about the system in coming weeks.
Vince and Juliet Moringiello both mentioned that they are on the publications board for Business Law Today. They mentioned that cyberspace topics are much desired for that publication. We could provide the full-sized article of about 3000 words in the BLT format of chatty (no footnotes!), and there is now a smaller format of about 600 words that allows for very fast turnaround.
Rae Cogar and Tim Chorvat discussed their ongoing projects for the Electronic Evidence Working Group. They wish to develop a few short articles for BLT followed by a program for one of our future ABA meetings. Candace suggested that what we need to is find the angle for business lawyers, since otherwise we will be (a) taking on more than we as a committee could chew, and (b) our expertise is not as litigators but rather as business advisors.
(Editor's note: Many lamented that management is not willing to engage in these issues, assuming that this is a lawyer's, and more particularly a litigator's, problem. What gets business managers' attention? If something will cost them money. Remember that system auditing controls were a non-issue until Sarbox came along, and consumer privacy issues were a minor issue for senior managers until the PCI standards came along threatening a merchant's ability to access credit card systems. As the new Federal Rules of Civil Procedure roll out in the next few months, which will be addressing deep-level electronic data concerns in discovery, management will eventually realize this is a bottom line issue. We best be ready to advise once that happens.)
Vince Polley raised the possibility of a project to advise primarily in-house attorneys regarding their companyies' receipt of a National Security Letter from the U.S. government (as provided in the USA-Patriot Act). This proposal would be jointly operated with other ABA constituencies such as the ABA Standing Committee on Law and National Security and the BLS Committee on Banking Law, each of which have indicated interest in working with the Cyberspace Committee. A lively discussion followed, with a few war stories and the like. For the moment, Michael Power and Peter McLaughlin in the Privacy Subcommittee will take the lead on organizing a project, although we will still be thinking about whether this is best in a particular subcommittee or organizing a task force, and maybe even setting up the task force as joint with other ABA groups. -- Stay tuned, but there was clearly a topic of great interest to this group.
Judie Rinearson opened up discussion of her sub-committee's work on how anti-money laundering laws (AML) will impact stored payment systems. Again, we pointed out that we should be looking to collaborate with other groups, such as Consumer Financial Services. Judy heard from others who offered help.
Candace announced that the upcoming Winter Working Meeting will be held in Little Rock, Arkansas. ABA is about to sign a contract with the Doubletree Inn in downtown. We will be pushing committee leadership to plan well ahead. Note that because the Spring Meeting in DC will be March 15-18, which is earlier than usual, we may well be too late at the WWM to prepare materials for Spring. (Unfortunately, we don't have hard deadlines yet, so this is surmise for the moment.)
Candace asked folks who participated in the prior day's CLC meeting, which was the "Un-Conference" format for setting up substantive discussions around the round table. All who were there yesterday thought it was a great exercise. One comment was that the size of the audience was probably important to how it worked, and that a typical full-sized CLC meeting would probably be too large for the format to work.
Candace mentioned the committee is being asked to provide a beta-testing group for the upcoming replacement of the ABA's listserve system (using the Fusetalk platform). A couple of the subcommittees volunteered to be guinea pigs. We will be learning more about the system in coming weeks.
Vince and Juliet Moringiello both mentioned that they are on the publications board for Business Law Today. They mentioned that cyberspace topics are much desired for that publication. We could provide the full-sized article of about 3000 words in the BLT format of chatty (no footnotes!), and there is now a smaller format of about 600 words that allows for very fast turnaround.
Subscribe to:
Posts (Atom)
