Tuesday, April 11, 2006

Yet Another Candid Camera Moment from Roland

My -- I give this guy the right to post and he just goes way overboard...

(Many thanks to Roland who really did a great job of adding to our blogging output this meeting. Let us all encourage him to continue, and to bring along that cool little camera of his as well. Here's a shot taken at the Carlton Fields reception outside the Yacht StarShip.)

Saturday, April 08, 2006

A few glimpses from the Columbia Restaurant -- The Committee Dinner

Michael Fleming and his daughter


Ray Gustini


Juliet Moringiello


Jonathan Armstrong (leveraging his British accent)


We {heart} Ziff


Sometime around 2001 as I was walking from one subsubsubworking group to another, at the Cyberspace Winter Working Group meeting at the DC Capital Hilton, I ran into this woman who was cruising the emptying room picking up the handout at the end of a session. (You know, the I-was-in-one- meeting-but-there-was- this-other-one- I-really-wanted-to-see- so-I-dropped-by-the-room -to-see-if-they-left- any-handouts ABA scavenger hunt. C'mon, don't tell me you don't do it too.) Literally ran into her, and I think I had to pick up the pile of paper we both dropped. I gave her the short version:

(insert Polley inflection here, boots optional) "Cyberspace Committee, ABA, Internet, all kinds of new law, e-commerce good, people good, fun good, publications pretty good."


I got most of the details wrong -- a point of which she still reminds me ("you said it was TWO years as chair! You LIED!") pretty much every ABA meeting -- but we hit it off anyway. Only thing I did right was to reflexively reach out to a newcomer. But hey, she bought it -- and became a wonderful leader, key Cyberspace author, replaced me and outdid me, and herself became the incubator of a bunch of additional really good leaders.


Today is her last day as E-Commerce Committee chair and we should celebrate her successes. Luckily someone booked us into a Cuban bar for dinner tonight... See you in Ybor City.

Afternoon Excursion (before Cyberspace Committee Dinner)

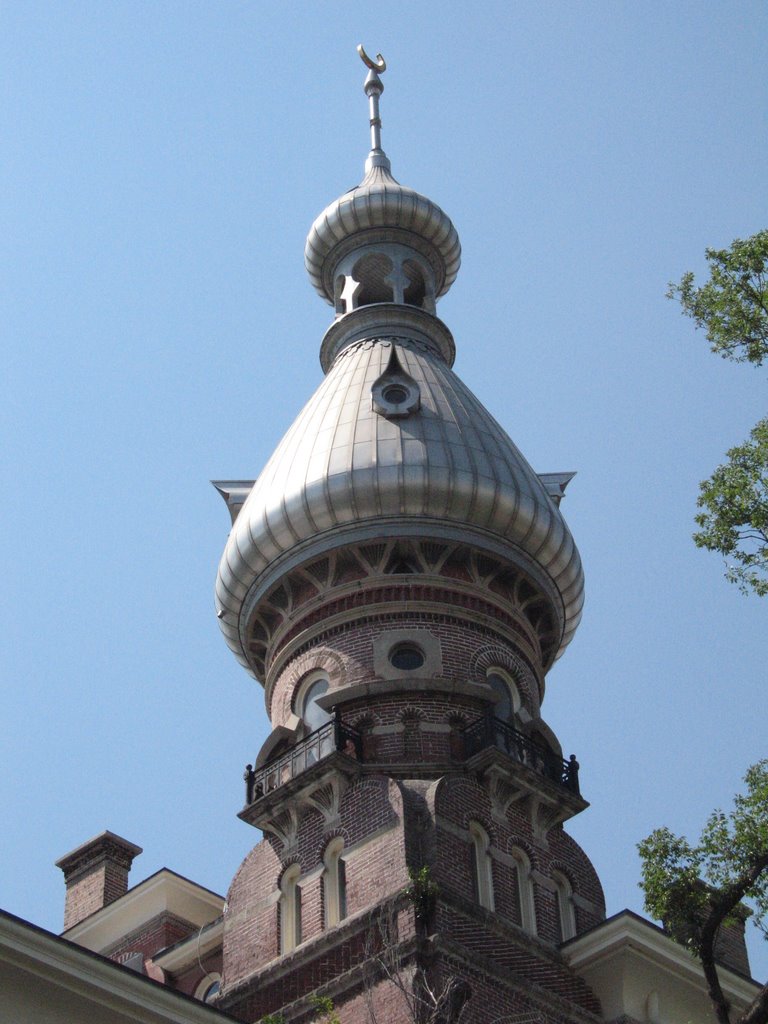
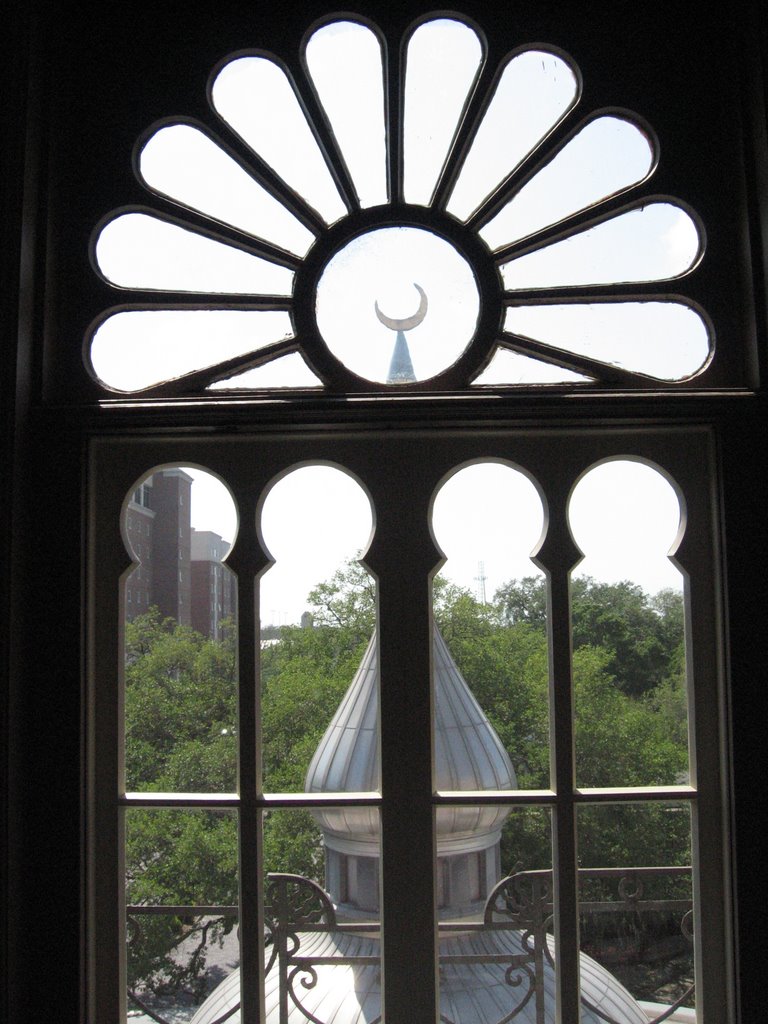
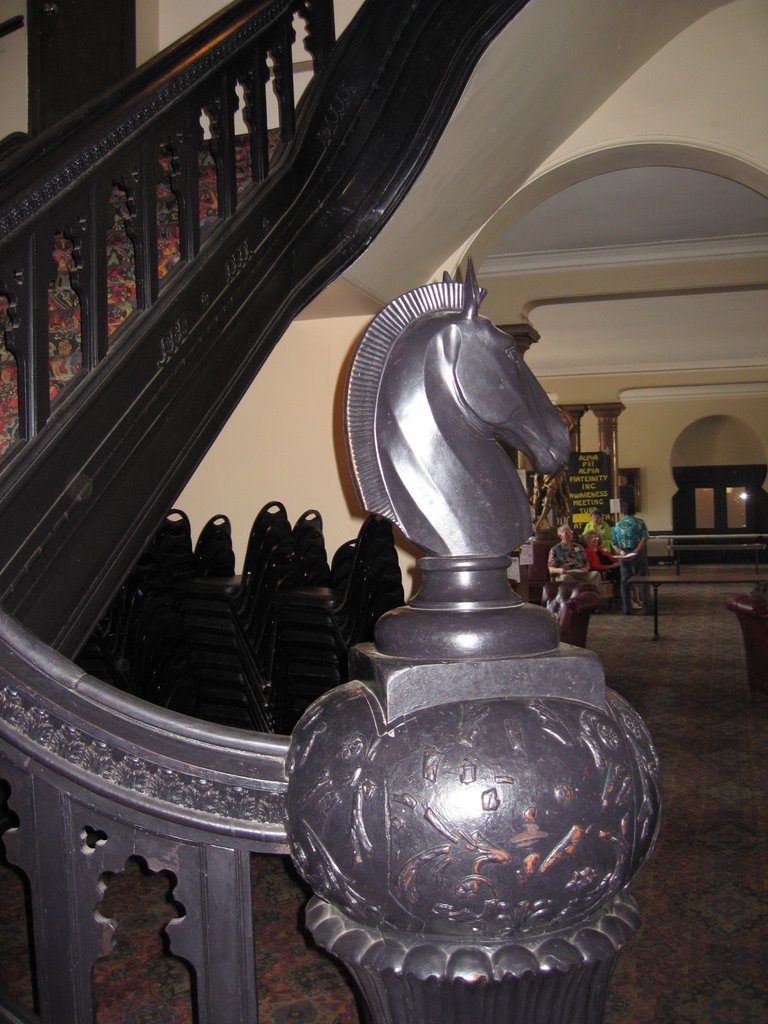
An intrepid group of cyberspace counsel fortified themselves with water, sunscreen and umbrellas and walked (some would say trekked) to the nearby Henry B. Plant Museum and its exotic architecture. Photos are better than words to describe the Museum, which was formerly a railroad hotel and is now known as Florida's First Magic Kingdom.


PROGRAM: 21st Century Risks and Age-Old Insurance Clauses

Bill Denny led a very interesting program how businesses are responding (or, in many instances, not responding) to the risks arising out of participating in cyberspace.

Mike Rodman of Albert Risk Management Consultants spoke on his observations of businesses and how they interact with the need for cyber-insurance. He noted a number of risks that should be addressed in any useful policy, particularly noting the need to address what things are NOT covered in other policies such as CGL. He suggested that there is still a lack of belief in the need for these kinds of cyber-loss policies -- and that in his opinion businesses do that at a higher degree of risk than they believe.

Bill Denny spoke on traditional contract principles and how we have historically allocated risks in IT deals. He then recalled the traditional insurance policies that we might have been analyzing for our clients -- third-party liability policies including CGL and its cousin E&O to cover many traditional IP claims such as copyright infringement; and first party coverages such as property, automobile and the like. He reminded us of the differences between occurence policies versus claims-made policies. He also reminded us of how some policies provide defense, some do not, some will pay defense costs after the claim is actually paid out, some count defense costs against the policy limits while others do not. Bill also went over how much of the boilerplate provisions we frequently glaze over may be self-defeating of our purported intentions.

Margaret Reetz of Chicago discussed how the newer policies have been working out in practice, based on her practice representing insurers. She discussed concepts of how the cyber-policies provide coverage, and misconceptions that are out there.

Emily Freeman of JLT Risk Solutions of London discussed how so many of us will spend so much time negotiating the best indemnity clause ever written, and never take the time to wonder if the indemnifying party has any insurance to stand behind that indemnity. She reminded us again how 'useless' CGL policies will be to cover indemnified cyber-risks. She also reminded us of how little consistency there is between the various policies that fall into the so-called cyber-policies. Her strongest message was that we should never rely on just calling out the name of a policy (like "CyberInsurance") and assuming that any particular risks are covered. (Emily has a checklist she would be willing to offer that lists the various risks that we should be asking about.) Rather, we need to cite the specific risks that need to be covered. She discussed the methods that potential insureds will need to follow to get coverage, including the due diligence that insurers will do prior to writing coverage. (Getting coverage, and 'passing' due diligence by the underwriter, is itself a flag for customers of the insured parties. Failure to get insurance can be a red flag.) She also noted that those who rely on their vendors to be the sole source of potential assets to cover risks are potentially foolish. The sorts of claims involve actions that tend to harm many parties -- Imagine a privacy breach that causes thousands of consumers who have dozens of different banks, all of whom use a common financial data services provider. If that provider has a $5 million policy, there is not much left for the 2nd claimant after all 4 dozen of them suffer $5 million in damages. Those customer businesses will hope they had through to obtain their own policies.

Working Group on Consumer Protection

The Consumer Protection group opened its discussions on how it will be participating in the ABA project to put up safeselling.com. The group will be adding much from the consumer's perspective, including needs for sellers to analyze and address the Magnuson-Moss Act's consumer warranty requirements as well as methods to disclaim certain warranties.

Touch base with Prof. Don Clifford if you wish to participate -- His Working Group's home page can be found here. This is a really great opportunity for the person who wants to get started with CLC, since the project lends itself well to one who wants to write both short or long pieces. See

Corporate Aspects of Information Technology (CAIT)

The CAIT subcommittee met on Saturday morning, chaired by standing Chair Don Cohn. First order of business, Don introduced the incoming new Co-Chair Bill Denny of Potter Anderson in Wilmington. Don and Bill have worked together for many years, and are looking forward to carrying on their work in the Committee.

Don ran through a number of projects that are in various stages of life, and made sure that potential participants knew that their mission was to get in touch with Bill or Don and get their wishes known.
  • An M&A checklist for IT concerns (Bruce Doeg & Bill Denny are leading the charge.) Can we assist the business community to understand the issues in IT that will come up in their deals? How can we get experienced lawyers in line when these deals come up?
  • How can the IT purchasing community start to get vendors to take contractual responsibility for the security breaches caused by their products?
  • Corporate-sponsored blogs -- Can we produce a product to advise counsel on analyzing the risks of issuing corporate-sponsored content via 'blogs' (or any of the other non-traditional mechanisms that we see now or that will surely be invented soon).
  • Corporate rules on how to filter incoming e-mail going to employees -- The USA perspective is essentially that the employer is in total control of this, but EU and other jurisdictions feel differently. How can a company that crosses boundaries have a viable policy?
Please get in touch with Don or Bill if you have any interest in adding efforts to any of the above.

Participants in the CAIT subcommittee meeting (chaired ably as always by Don Cohn)

Candace Jones and Vince Polley

(photos by Roland Trope)

Next Year's WWM

Candace announced at the plenary sessions that we are tentatively a GO for meeting this coming January in member Elizabeth "Soon-to-be-a-Mom" Bowles' home town of Little Rock, Arkansas. (Elizabeth later reminded us that while most of the locals refer to themselves as ar-kan-sans, the state constitution officially denotes them as ar-kan-sawyers.)

This is another great opportunity to enjoy the home city of one of our members (just as we did this year with Bill Denny and Don Cohn welcoming us to Wilmington and the wonderful Hotel DuPont). I am looking forward to seeing a town I've yet to spend time in.

Model Data Breach Notification Procedure and Payment Card Industry information Security Standards (CLE session)

Panelists: Joan Warrington (off cam); Michael Power; Robert Rothman; Jon Armstrong; Tom Laudise (moderator); Peter McLaughlin and Hank Judy (off cam)

Panelist: Jonathan Armstrong (delivering his presentation)

Panelist Joan P. Warrington explained PCI Data Security Standards


Questions from the audience were lively.

Panelists provided an unconventional discussion to company responsibilities to fulfill statutory obligations when data breaches occur.

Tom Laudise noted that the California statute (the "grand daddy" of data breach reporting statutes) overlooks the fact that with web search capabilities, data thieves do not need several kinds of personal data, they need only one important kind such as social security number and can then locate the rest of the data they need in order to make illicit use of the data.

Tom also noted that with so many states now having enacted disparate data breach statutes, it is time for federal legislation to harmonize these obligations. He discussed the pending HR 4127, Data Accountability and Trust Act, and its underlying theme "If you can't protect it, don't collect it." It gives enforcement action authority to the FTC and state attorney generals, which is strongly opposed by financial service companies. He doubts, however, that unless there is a significant data breach for a triggering event that the House will enact any of the competing bills currently pending.

Jonathan Armstrong, from the UK, discussed data breach -- a view from Europe. He noted that there are increasing numbers of data breaches in Europe, and particularly in the use by EU businesses of offshore call centers. He noted that companies seem reluctant to recognize that if you pay employees less, you increase the chances that they will be susceptible to bribes by data thieves. He drew an analogy to a weather map, and noted that there is a strong storm system of threats to data privacy moving west from Eastern Europe. He also provided the graphic example of a person who once told him "you will never understand data privacy until a neighbor of yours has been taken out and shot." Jonathan noted that despite the EU-wide Data Directive, each Member State has implemented its own national version, and that the prosecuting official for a data breach will, therefore, not come from EU headquarters in Belgium, but from the local Member State. In Europe he added that there is "loads of law, but little enforcement", whereas in the US "you have little privacy law, but vigorous enforcement." Mandatory reporting requirements are proliferating, with Norway being the first, where the mandatory report must be to the Norwegian data commission, which then will decide if the company must report to end-users or affected customers. Data reporting laws also have emerged in Hungary, Malta, Sweden and Germany. In most countries, persons have the right to make a "subject access request" -- if they believe they are in a class affected by a data breach, they can submit such a request, and the company must respond within a brief period. In Europe, it is common that prior to handling personal data, a company must register with the Member State's data protection commission.

Robert Rothman emphasized the need during initial diagnosis of a data breach to create a centralized "Fact Sheet" to ensure that one version, not many, becomes the view of the company internally and in contacts with the media. He pointed out that when a company reports a data breach it should give very careful consideration to omitting from such notice any disclosure of information that would alert the data thieves to the significance or value of the platform or stored data that they took.

Michael Power approached the problem as an evidence collection exercise in which the overseeing counsel need to make sure that they can trust everyone involved. He noted this must start with the engagement of a forensic expert. When a company suspects a known person or target who may have stolen the data, he recommends seeking court orders to compel production of their storage devices in order to "ghost" them and review contents to determine if they contain stolen data. He drew the analogy to coming home at night, finding the door had been forced open, and then you have the difficult task of determining what happened -- did the intruders merely walk around, did they party (unlikely), did they go upstairs and take valuables from drawers, etc. Finding out what the data intruders actually did is an important task that needs to be investigated and should not be assumed away. He noted unique issues that arise under Canadian federal and provincial privacy laws. In one instance, he discussed how the team leader (and there MUST be one after a breach) needs to be prepared to deal with the media. He echoed the theme of earlier panelists "Get the Lawyer in Early" if there is a security breach.

Joan Warrington elaborated on that theme emphasizing the risks of class actions and attorneys general investigations. She devoted considerable attention to the Payment Card standards and how clients will increasingly need to grapple with these standards. They emerged, in part, from Visa, which have been approved and adopted by all of the big payment card sponsors -- Amex, MasterCard, etc. They are applicable to all entities that store, process or transmit card holder data. If you go to the websites of these card issuers there are inches thick materials (when printed in hard copy) on compliance with those standards. Several banks, for example, have sued BJ's claiming that they are third party beneficiaries of those standards and seek to recoup funds lost through thefts that originated in data stolen as a result of BJ's alleged failure to comply with those standards.

Hank Judy encouraged counsel to download from the Better Business Bureau and from MISMO websites the primers available on how to handle data breaches (the former is best suited to small businesses, the latter provides a more sophisticated and technologically advanced guide). He highlighted certain issues that can be easily overlooked. Unlike usual thefts where missing items mean something has been stolen, with data "the absence of evidence is not evidence of absence" because hackers are often skillful at compromising data without leaving a trace of their intrusion and leaving the data seemingly intact. There needs to be a person with "unambiguous decision-making authority." Although perhaps counterintuitive to companies fearful of the consequences of a public disclosure, he encouraged the use of a website to provide notice (gets the word out to a wide community, and keeps control of the version released by the company -- and allows a company to combine a good account of the incident, with links to service providers that can help consumers protect themselves from the consequences of the breach, and that allows a company to continuously update its account and such aids as needed). Hank recommended as an example that counsel view a few websites, including this one put out by Georgetown University after an incident.

Questions from the audience, including Michael Khoury's inquiry about how to respond when you advise your client on the best practice responses to the data breach and brings you up short with one or another version of the question, "But isn't that going to cost us a shitload?"

Subcommittee on Privacy, Security and Data Management

Michael Power and Peter McLaughlin co-chaired this morning's meeting of the cyberspace subcommittee on Privacy, Security and Data Management. More than 35 people attended (and more than half of them were new to the subcommittee). There was discussion about possible new projects -- e.g., collection of examples of negotiated clauses/exceptions to standard software vendors' exclusion of liability for security breaches (and/or a collection of examples of how large buyers have used their buying power to move vendors away from their historical hard line). There also was discussion about CAIT's ongoing project to develop (and keep up to date) a set of checklists/tools to help counsel effectively work through the barrage of decisions that have to be made while in the midst of a security incident (e.g., a network security breach).

Andy Serwin made a presentation (using powerpoint in an unexpected way, with non-volatile storage/display tools -- paper) trying to read the tea-leaves about the FTC's emerging security policies. While recent enforcement actions are reported as "privacy-protection" activities, a closer look suggests: (a) the FTC is more focused on lacking underlying security, at (b) companies that are holding financial-related information. Relying on Gramm-Leach-Bliley, FTC has seized on the lack of a written contingency plan (for managing security incidents). (While many companies have at least decent security processes, many of these aren't formally enough institutionalized in a fashion that facilitates knowledge continuity -- hence, the need for a written plan.) FTC actions also illustrate the need for formalized, risk-assessment and risk-management processes, being systematically applied to the area of information security. (An ecopy of Andy's presentation resides here.)

The number of people in the room, the kinds of questions raised, and the level of passion exhibited during this meeting all suggest that the "perfect storm" of security/privacy is closer than a distant speck on the horizon. The lawyers who prepare earliest may actually benefit from the coming storm, by being able to out-sail their less-well-prepared colleagues. As with Health-Safety-Environment, companies also may find an emerging competitive advantage flowing from their earlier planning. (Argue this, when justifying your participation in our work.)